Oracle’s October Patch Update Covers 1,295 Vulnerabilities, Including Six CVSS 10.0 Flaws
Oracle patched 1,295 vulnerabilities in October. Six carry CVSS 10.0 scores, with unauthenticated network access at the center of several.
Data analysis, big data, and business intelligence
Found 351 articles
Oracle patched 1,295 vulnerabilities in October. Six carry CVSS 10.0 scores, with unauthenticated network access at the center of several.
Dual BIOS can restore a laptop after corrupted firmware, helping small businesses limit downtime when recovery tools and reinstalling an OS aren’t enough.
A New Mexico judge cites more than 43 million consumer protection violations in a $25 billion Meta judgment over access to Facebook user data.
AI can uncover and exploit flaws at machine speed. Security teams need faster exposure triage, patching and containment, backed by stronger fundamentals.
Wearable recorders make AI note capture harder to spot and govern. Companies need clear rules for disclosure, retention, vendor security, and transcript review.
PHP2Shell exposed the risks of early patch leaks as attackers probed PHP systems before public disclosure. Security teams need asset visibility and day zero detection.
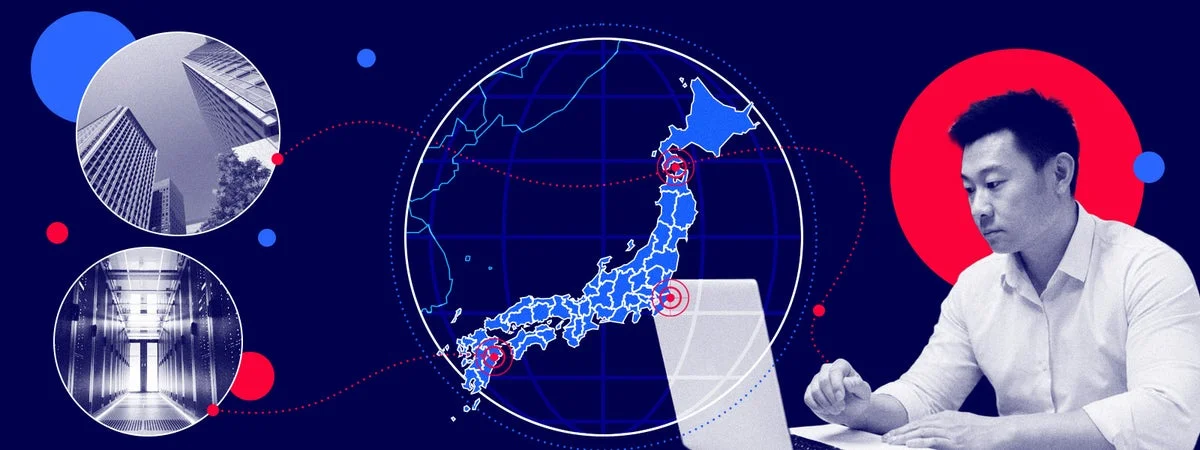
Reports of cyberattacks on Japanese entities jumped 48% from Q2 to Q3 2026, with shared providers widening disruption and new disclosure rules taking effect.
Stolen UpdraftCentral keys let attackers install persistent backdoors on connected WordPress sites, leaving admins with cleanup beyond credential revocation.
AI can find complex vulnerabilities quickly, but safe remediation depends on sandbox testing, environment context and tightly scoped permissions.
PwnEscape uses guest-controlled checksum metadata to corrupt IPv4 packet headers, exposing host memory and enabling root code execution on vulnerable systems.
The October attacks show why refrigeration security depends on contractor access controls, alerts for remote changes and plans to replace unsupported controllers.
Long-lived sensitive data and hard-to-update equipment complicate post-quantum security. Device inventories, protected gateways and vendor roadmaps can guide migration.
Three NGINX flaws rated 9.2 could enable crashes, denial of service or code execution. F5 urges customers to patch and audit configurations.
A Microsoft and Nvidia framework maps 30 risks and urges provenance checks, configuration testing, and ongoing safeguards for open-weight AI deployments.
A newly identified flaw in OpenAI's skills repository raises concerns about supply chain security in AI applications, emphasizing the need for careful vetting.
Xbow USA utilized AI compute time worth $40K to uncover critical vulnerabilities in Chrome, leading to a $250K bug bounty from Google.
A significant vulnerability in the Linux kernel allowing guest-to-host escapes through the networking stack has been resolved, strengthening security protocols.
A recent zero-day vulnerability in BeyondTrust’s Remote Support software has raised alarms, allowing attackers to gain root access and control over user systems.
TypeSafe's Jev artificial intelligence model, designed for rapid machine-to-machine communication, is found to be more susceptible to attacks than traditional LLMs.
Cisco's Secure Email Gateway is vulnerable to exploitation, allowing attackers root access; updates are available, but vigilance is essential.