GitLab Patches Critical Regex Flaw and LDAP Account Takeover Risk
GitLab’s updates fix an unauthenticated code execution flaw and an LDAP account takeover bug, with implications for dependent software and AI tool trust.
Development operations, CI/CD, and automation
Found 105 articles
GitLab’s updates fix an unauthenticated code execution flaw and an LDAP account takeover bug, with implications for dependent software and AI tool trust.
GitLab has released critical security patches for a maximum-severity vulnerability and five additional high-risk flaws affecting its platform.
Explore how a shared P2P cache improves efficiency in multi-tenant Kubernetes environments while reducing redundant data storage.
Denmark's review of its national ID system follows unauthorized access affecting 8.8 million individuals, prompting calls for stronger identity verification.
Microsoft's release of WSL containers streamlines Linux development on Windows, eliminating common integration challenges for developers.
The domain third-party[.]com is luring users into malware traps, raising alarm for those using it in documentation and code examples.
GitLab's project email feature puts repositories at risk due to poor security practices, allowing unauthorized modifications if addresses are leaked.
Russia intensifies its hybrid warfare tactics across Europe, putting critical infrastructure and organizations at heightened risk for sabotage and cyber attacks.
Outdated GitHub App private keys can remain valid indefinitely, creating significant security vulnerabilities for organizations if not proactively managed.
A newly discovered GitLab vulnerability enables unauthorized file access, impacting many enterprises; immediate action is essential for protection.
A bidding war over Spirit Airlines' employee data intensifies as Micro1 offers $12.5 million following Google's recent $10 million acquisition bid.
Kubernetes 1.37 introduces substantial improvements in dynamic resource allocation and API validation processes, enhancing efficiency for AI and HPC workloads.
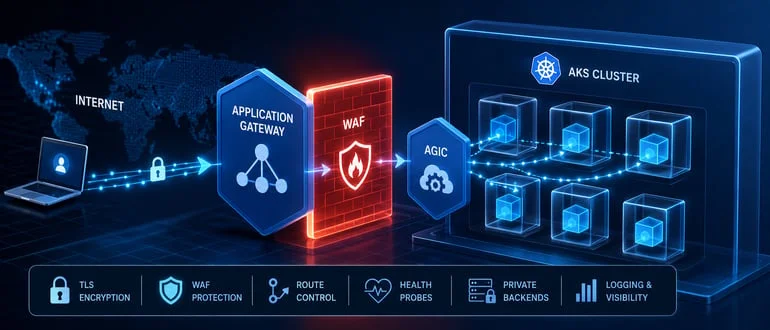
Securing the ingress layer is vital for protecting Kubernetes workloads; integrating Application Gateway and WAF can significantly enhance security against threats.
Evaluate cloud-native platform components critically to reduce complexity and enhance operational efficiency, ensuring each element justifies its existence.
Master on-prem Kubernetes networking with direct routing strategies to simplify management, improve visibility, and enhance operational efficiency.
A serious flaw in GitLab exposed repositories to unauthorized modifications, prompting urgent updates for all users to enhance security.
A recent trojan attack on AI skills has led to over 1.7 million downloads, exposing vulnerabilities in the AI software supply chain.
Google's introduction of a new naming convention for cyber threat actors raises questions about its effectiveness in promoting clarity in cybersecurity.
The recent US ban on foreign-manufactured robotic devices, including robot vacuums, poses significant challenges for the industry.
Rumored for months, Samsung’s “Galaxy Buds On” have shown up yet again with an open-ear design, but the bigger question at this point is when they’ll actually debut. The folks over at SamMobile uncove...