Malware Exploits Microsoft Ecosystem for Covert Command-and-Control Operations
A new Python malware framework, TWINLOOT, leverages Microsoft services for command-and-control, complicating detection and response efforts.
Rapid internal communications during a cyber breach can turn against companies, affecting legal privilege and leading to severe repercussions.
Greg Brockman emphasizes the urgency for enterprises to adopt agentic AI tools for cybersecurity, while industry experts criticize his recommendations as lacking depth.
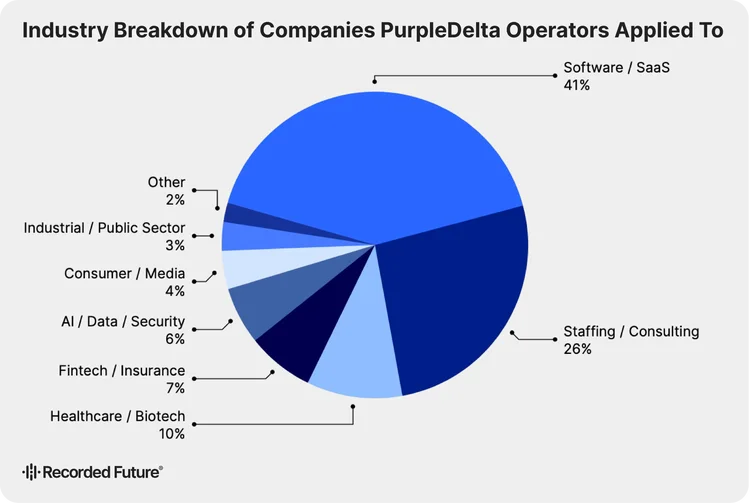
Uncover significant tactics used by PurpleDelta, a North Korean operation infiltrating global job markets with deceptive persona management and real-time AI tools.
Data quality significantly impacts AI's effectiveness in security operations, often proving more important than model selection for optimal outcomes.
AmnesiaStealer malware exploits fake GitHub pages to hijack browsers on macOS, enabling attackers to control victim sessions and harvest sensitive data.
Future CISOs will transform into strategic facilitators and enablers of business, balancing innovation with risk management by 2029.
Researchers highlight a new wave of data breaches targeting Salesforce and ServiceNow, signaling the need for enhanced security measures.
Oracle's new free security tool helps organizations monitor database vulnerabilities, a timely addition amidst increasing cyber threats.
Akira ransomware has leveraged Windows Safe Mode to evade endpoint detection, but encountered operational setbacks during its execution.
Properly assigning roles in cybersecurity can significantly mitigate backlogs, enhancing accountability and effective risk management.
Cybersecurity leaders are evolving into strategic partners, focusing on innovation and resilience to drive organizational growth and confidence.
Researchers have uncovered active exploitation attempts of a zero-day SQL injection vulnerability in the widely-used GeoServer platform, necessitating immediate action.
A new report reveals vulnerabilities in Microsoft SCCM, emphasizing an ongoing risk to enterprise servers despite recent patches.
Microsoft emphasizes the need for a paradigm shift in cyber defense strategies due to the rapid rise of AI-generated vulnerabilities.