VeloCloud Orchestrator Vulnerability Exposes Critical Flaw, Urgent Patching Required
A serious vulnerability in the VeloCloud Orchestrator allows remote attacks, necessitating urgent patches for affected versions to prevent exploitation.
Cloud platforms, services, and infrastructure
Found 39 articles
A serious vulnerability in the VeloCloud Orchestrator allows remote attacks, necessitating urgent patches for affected versions to prevent exploitation.
Z.ai disables its ZCode coding assistant's feature after it inadvertently uploaded user code to cloud servers, sparking major security concerns.
Revoking access tokens may not suffice to eliminate threats; new strategies for incident response are essential against evolving cloud-based attacks.
Recent probing of Vite servers for cloud credentials underlines significant security vulnerabilities in the JavaScript ecosystem, with urgent updates needed.
Exaforce enhances its AI Security tool to monitor a wider range of AI agents, leveraging existing security telemetry for more effective threat detection.
Microsoft's Teams and M365 services are shifting to new URLs, requiring companies to update their network configurations for uninterrupted access.
A fake Cloudflare verification on an STPI website injects a malicious command into user clipboards, posing risks to IT professionals and their systems.
ServiceNow is evolving its strategy by embracing AI and cybersecurity, shifting from traditional subscription models to consumption-based services.
A new phishing campaign exploits passkey themes to access Microsoft 365 accounts, emphasizing the need for stronger MFA practices.
Researchers uncovered a security flaw in ChatGPT that allowed attackers to extract data from connected Gmail accounts without user awareness.
Mars Security's latest feature streamlines the translation of threat intelligence into actionable detection rules, drastically reducing response times for security teams.
Cybercriminals use AI agents to execute ransomware attacks in under 10 hours, challenging traditional cybersecurity measures and requiring urgent adaptation.
Anthropic's Enterprise Frontier Safeguards empower businesses to control data monitoring while detecting AI misuse, balancing compliance and security.
A sophisticated attack campaign uses counterfeit CAPTCHA prompts, leading victims to execute harmful commands that compromise corporate networks.
Modern cloud-native environments demand a shift from traditional GRC models to continuous assurance, enabling real-time compliance management.
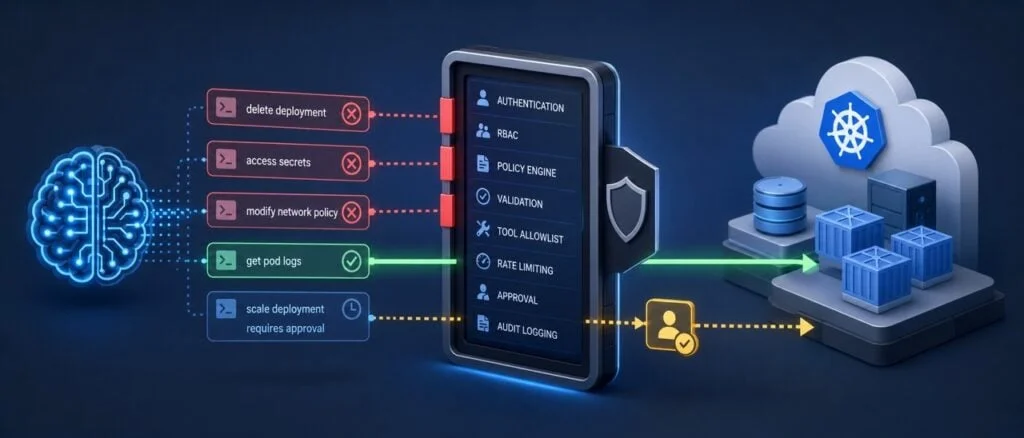
Prompt injection threatens cloud-native AI systems; teams must rethink access control to prevent infrastructure vulnerabilities.
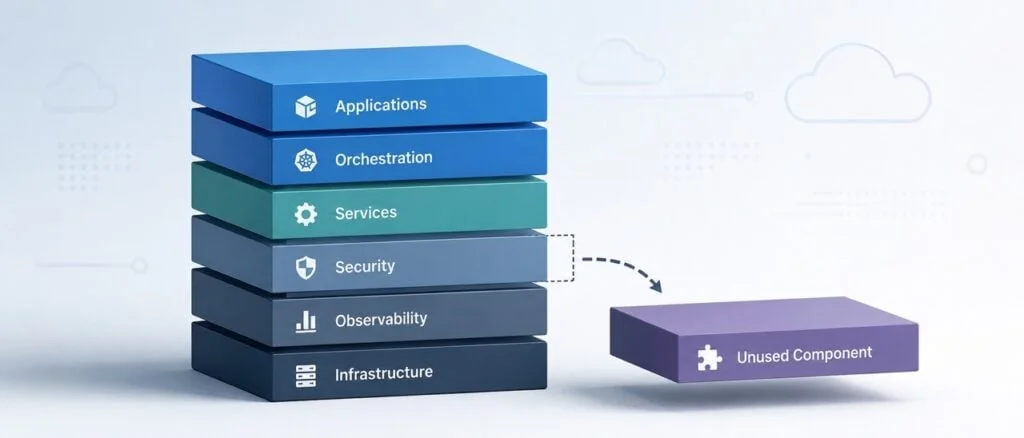
Evaluate cloud-native platform components critically to reduce complexity and enhance operational efficiency, ensuring each element justifies its existence.
A series of compromised Rust packages introduced backdoors that executed malicious code during compilation, exposing developers to significant risks.
Citrix's recent advisory highlights critical vulnerabilities in NetScaler devices. Security experts stress urgent patching to prevent potential exploits.
Recent supply chain attacks in AI development highlight significant vulnerabilities. Here's how to safeguard your environment effectively.